Why NIS2 Will Reshape Cybersecurity for European Firms
NIS2 makes senior management personally liable, expands scope to thousands of new companies, and requires incident reports within 24 hours. Most mid-market firms aren't ready — the clock is ticking.
Our Services
From strategy to certification, from board-level advice to hands-on testing — everything you need to build and maintain real security.
3rd Party Risk Management
We inventory and tier every vendor by risk, then dig into the ones that could hurt you — not a 200-question checklist for everyone. You get contracts with teeth and one programme that satisfies NIS2, DORA, and ISO 27001 together.
Board & Senior Management
Presentations and training that make cyber risk clear at C-level. We translate NIS2 and DORA's personal liability rules into plain language, so your board knows what it's accountable for — from executive training to confidential one-on-one coaching.
CISO-as-a-Service
Senior security leadership from a few days a month to full-time interim. Three tiers — CISOlite, CISOplus, and CISObridge — scale from a foundational roadmap to full crisis authority. You get Fortune 500 CISO experience, not a junior consultant.
Cybersecurity Strategy
A clear, risk-based roadmap connecting security spending to business outcomes. We assess real risk, then build a plan that hardens your defences without straining your team. We stay through rollout and training — until it's running, not sitting in a slide deck.
Governance Setup
Policies, risk frameworks, and governance structures people actually use. We work in five modules — from a quick assessment to a full ISMS build — so you start small and scale up. You get risk registers, KPI/KRI dashboards, and policies sized to your business.
ISO 27001 Fast Track
Real progress in 90 days — certification comes later. An assessment and ISMS build lock in your scope and governance within weeks. When you're ready, Fast-Track Complete carries you through implementation and audit to certification in 6–9 months, with 40+ templates.
NIS2 Compliance
Gap analysis and remediation to meet NIS2 on time. We classify you as Essential or Important, then close the gaps against CyberFundamentals with real controls. Board training and supply-chain risk are part of it too — NIS2 holds directors personally accountable.
Microsoft 365 Security
Hardened configuration, conditional access, and DLP for your M365 tenant. We review all seven domains of your real security posture, benchmarked against CIS Foundations and your Secure Score. You get a prioritised fix list plus same-day quick wins.
Penetration Testing
Realistic attack simulations that find what scanners miss, with clear fixes. Choose EXPRESS, starting within 24 hours, or Standard, covering nine systems from web apps to AWS, Azure, and SAP. Every test is manual and follows ISO 27001, NIST, and OWASP.
Training Catalogue
Awareness sessions, workshops, and board-level briefings for every audience. From NIS2/DORA liability briefings to hands-on OKR workshops, every session is led by people who've done the job — not trainers reading slides. Delivered on-site, remote, or hybrid.
We're Not Your Typical Cybersecurity Company
Boutique firm, senior practitioners, direct access — no layers of junior analysts in between.
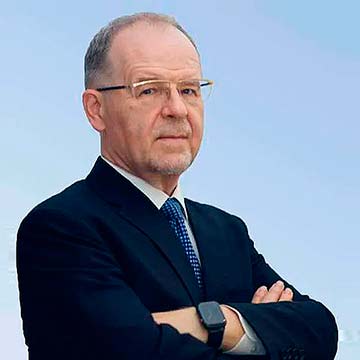
Cubic Consulting is a boutique firm built on one principle: you should work with the person doing the job, not someone relaying messages on their behalf. We're led by a senior practitioner with hands-on CISO experience across Fortune 500 companies, financial services, and critical infrastructure — and that's who shows up to your engagement, not a project manager, and not a rotating bench of junior analysts billing by the hour.
That experience is why our work holds up. We build security programmes that survive contact with reality: practical, proportionate, and shaped around how your business actually operates — not a template pulled off a shelf. No shelfware. No box-ticking. Controls your team will actually run.
We're based in the Benelux and work across the EU, fluent in English, French, German, and Luxembourgish, so there's no language barrier with your board, your regulators, or your technical teams. And because we've cut the overhead large firms carry, you get the same calibre of expertise for 30–50% less than Big Four pricing.
How Cubic Consulting Helps
Security isn't a product you install — it's a capability you build. We help at every stage.
Assess & Understand
We map your current posture — what's working, what's exposed, and what regulators expect. A clear picture of where you stand.
Build & Implement
Strategy without execution is a PowerPoint. We write the policies, configure the controls, train the teams, and run the projects.
Lead & Sustain
vCISO leadership, board reporting, vendor oversight, incident response — we stay in the chair as long as you need.
Not sure where to start? That's fine — most of our clients weren't either.
Book a Free Discovery CallHidden Dangers You Should Know About
Cyber threats don't always look like Hollywood hacking. These are the real-world risks that catch businesses off guard.
Over 90% of breaches start with a phishing email. Today's campaigns use AI-generated content, compromised supplier accounts, and pixel-perfect login pages designed to fool smart people under time pressure.
Security Awareness Training →Modern ransomware groups steal data before locking systems. Even with backups, they threaten to publish client data. The problem extends to regulatory exposure, reputational damage, and breach notification under GDPR and NIS2.
Build a Cybersecurity Strategy →SolarWinds and MOVEit showed what happens when attackers compromise a trusted vendor. Your security perimeter extends to every third party with access to your data. Most companies lack a structured way to manage that risk.
3rd Party Risk Management →Exposed storage, overly permissive admin roles, disabled MFA — these aren't sophisticated attacks, they're configuration mistakes. M365 alone has hundreds of security settings, and most tenants run on defaults that leave significant gaps.
Harden your Microsoft 365 →Not every insider threat is malicious. Employees forwarding files to personal email, using shadow IT, or misconfiguring shared drives can cause the same damage as a deliberate leak. Without proper controls and monitoring, you won't spot it in time.
Establish Governance & Controls →NIS2 introduces personal liability for senior management. GDPR fines keep growing. DORA applies strict rules to financial services. Regulators are actively enforcing, and "we didn't know" stopped being acceptable years ago.
Prepare for NIS2 Compliance →Let's Figure Out What You Need
Book a free 30-minute call. We'll talk through your situation, give you an honest assessment, and tell you where to start — or whether you need us at all.
Book Your Discovery CallLatest Insights
Practical takes on Penetration Testing, Cybersecurity and Crisis Management.
Latest Video
Stay Ahead Of Cyber Threats With Our Penetration Test
In this video we introduce our Penetration Testing services, designed to help businesses defend against cyber threats. Offering both EXPRESS and Standard options, we ensure dedicated support, expert insights, and comprehensive reporting.
Watch on YouTube →Watch all VideosLatest Blog Article
When “It Won’t Happen To Us” Becomes a €480,000 Lesson
A Luxembourg SME with 50 employees thought their size made them invisible to attackers. One phishing email later, they were staring at nearly half a million euros in damages. Here's what every small business needs to hear. A Luxembourg SME with 50 ...
Read more →View all PostsLatest Podcast
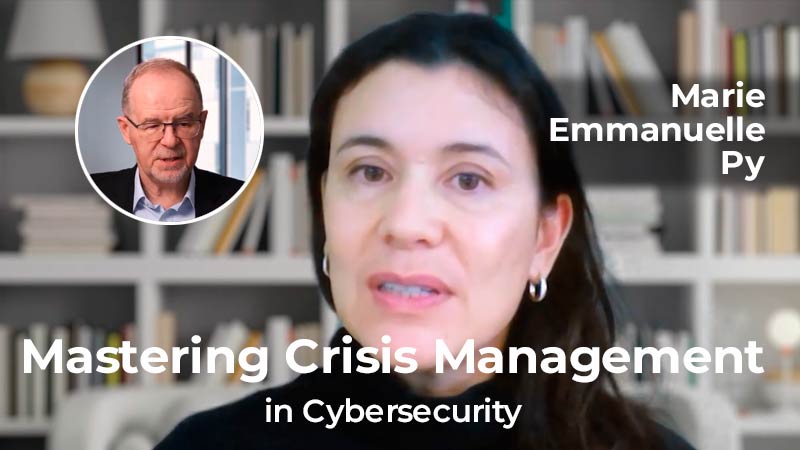
How To Enhance Your Cybersecurity Strategy
In the latest episode of the Cubic Lighthouse podcast, host Guy Marong engages with crisis management expert Marie Emmanuelle Py to explore the critical lessons for cybersecurity incident managers. The episode delves into Py's unique background, which includes ...
Listen to more →Listen to all PodcastsLet's Figure Out What You Need
Book a free 30-minute call. We'll talk through your situation, give you an honest assessment, and tell you where to start — or whether you need us at all.
Book Your Discovery Call